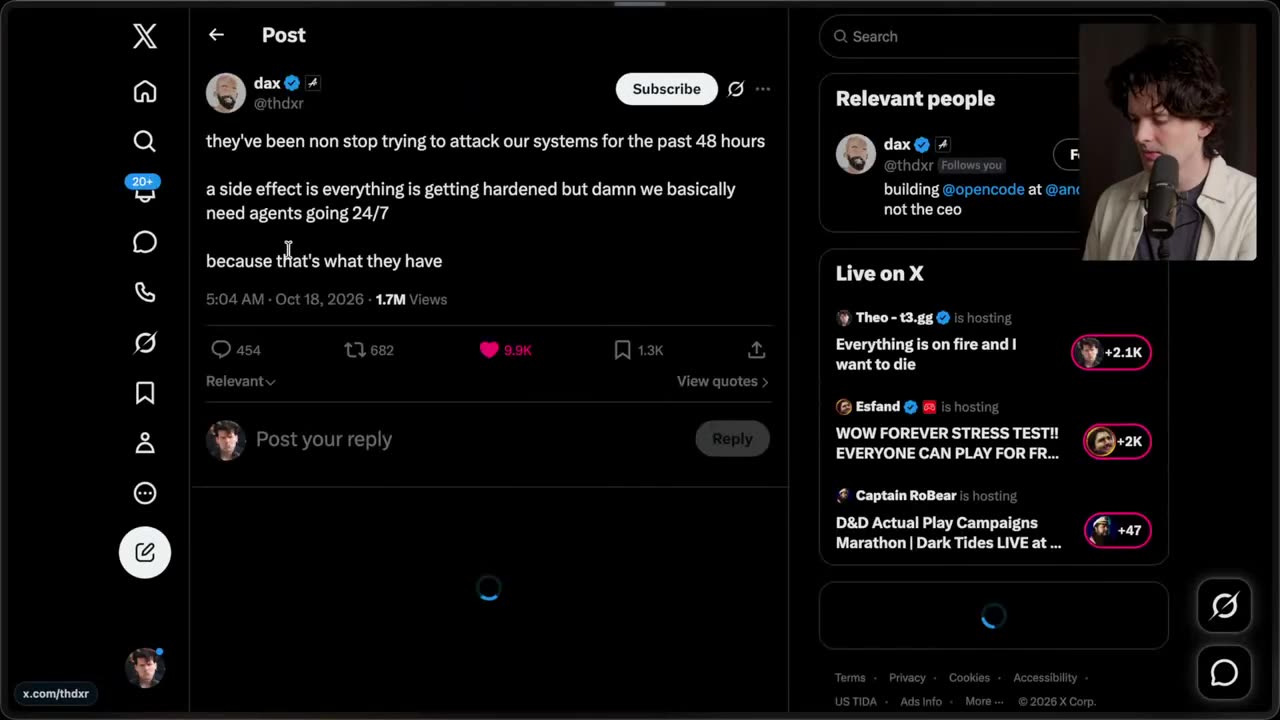
they've been non stop trying to attack our systems for the past 48 hours a side effect is everything is getting hardened but damn we basically need agents going 24/7 because that's what they have if you want to know the type of stuff we're dealing with here's an example the link is a planetscale oauth flow set to send credentials to an attacker we're seeing hundreds of completely different attempts every day vehicle mogging so hard rn he wishes he was me oops this is a chart crime a weird thing about OSS pull requests these days is we don't know what model was used for it and our internal setup provides better tools to the agent so they're almost always worse than sending the prompt ourselves it's mostly useful for environments we cannot recreate so they're almost always worse than sending the prompt ourselves it's mostly useful for environments we cannot recreate the amount of internal tooling is exploding, it must be at all companies a weird side effect is when you switch companies then it's all new tools you have to learn, way less consistency than before there's some incredible software i get to use because someone talented was able to finally prompt an idea on the side they never would have otherwise the amount of internal tooling is exploding, it must be at all companies a weird side effect is when you switch companies then it's all new tools you have to learn, way less consistency than before but also you can just use an agent to learn about them so maybe it all nets out
Did  Theo
mention me?
Theo
We scan every video for X posts on screen, then check the transcript to see if they were read aloud. See everything Theo showed.
Every post with your handle on screen. A profile or post link works too.
Matches the text of one post, even if the handle was cropped out.
A few words you remember. Matches by words and by meaning.
@thdxr
Yes.
Theo showed your posts 10 times and read 1 aloud.
-
dax@thdxr
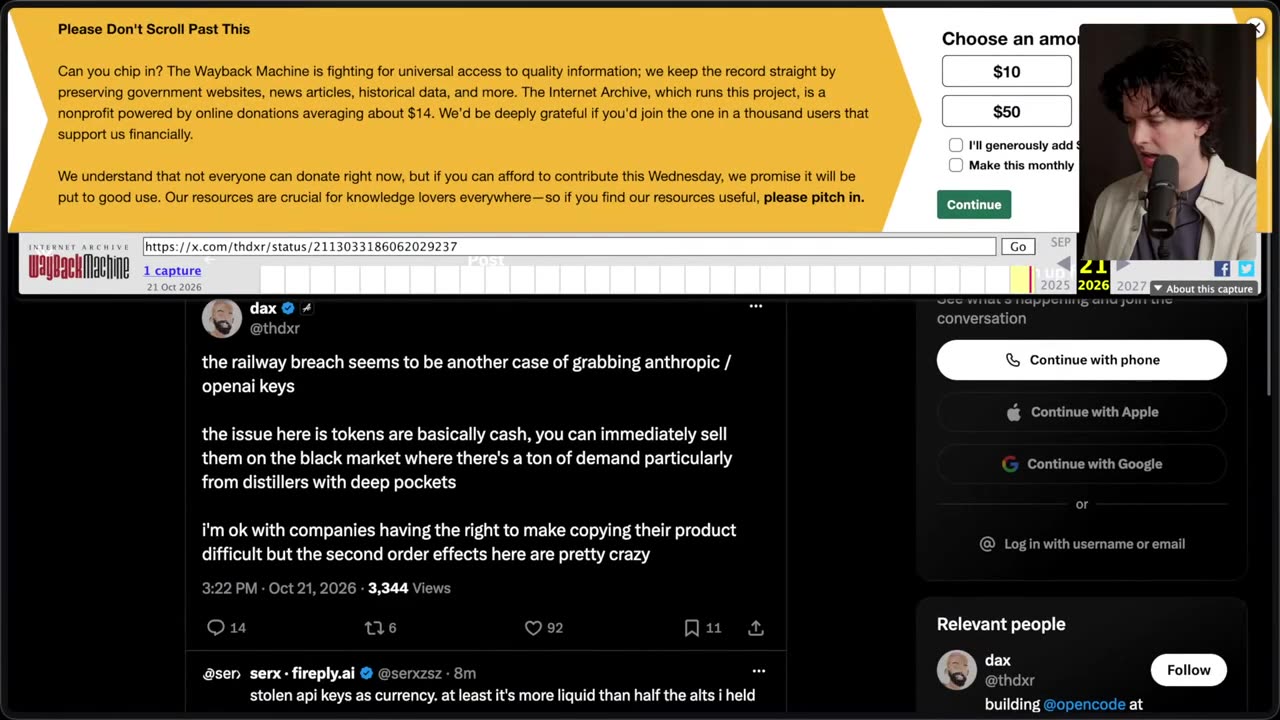
the railway breach seems to be another case of grabbing anthropic / openai keys the issue here is tokens are basically cash, you can immediately sell them on the black market where there's a ton of demand particularly from distillers with deep pockets i'm ok with companies having the right to make copying their product difficult but the second order effects here are pretty crazy
Theo read it aloud at 15:58 Dax clearly deleted that because it got him in trouble, so I don't want to post.
-
dax@thdxr
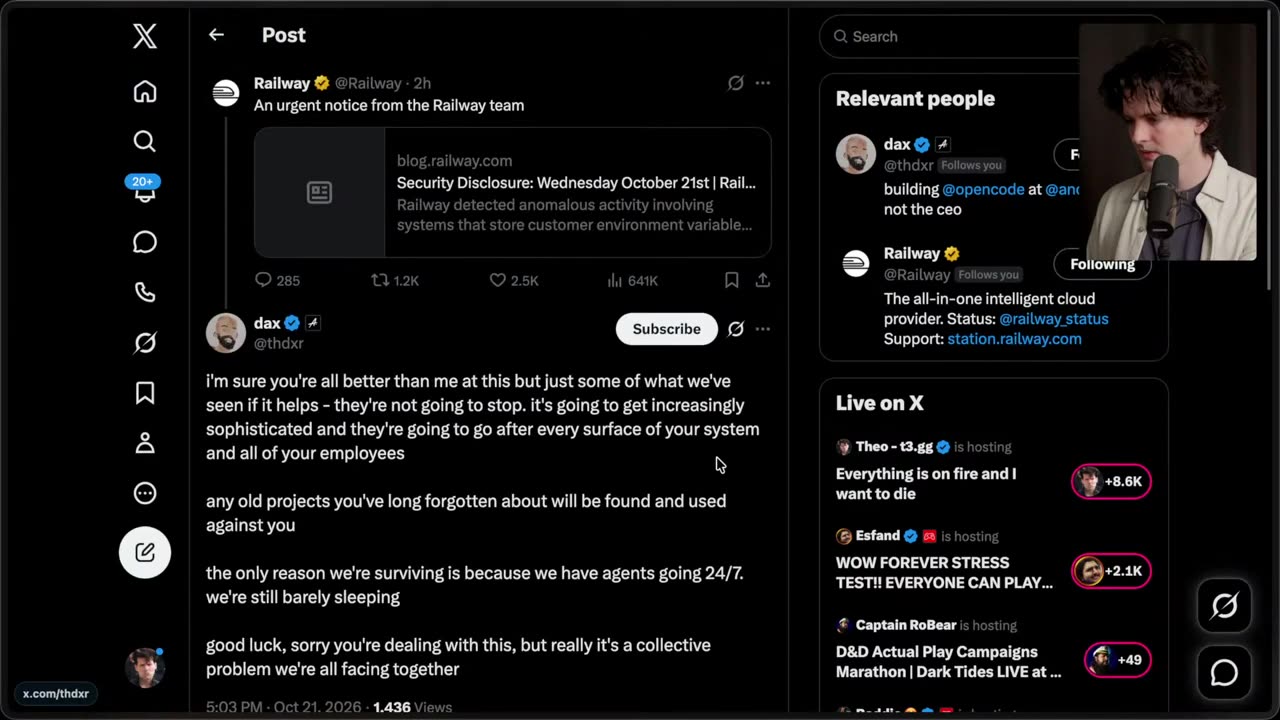
any old projects you've long I'm sure you're all better than me at this but just some of what we've seen if it helps - they're not going to stop. It's going to get increasingly sophisticated and they're going to go after every surface of your system and all of your employees any old projects you've long Show more any old projects you've long forgotten about will be found and used against you the only reason we're surviving is because we have agents going 24/7. we're still barely sleeping good luck, sorry you're dealing with this, but really it's a collective problem we're all facing together thanks Dax - we haven't been sleeping much on our side but it does seem like (personal opinion) we are in the 24/7 drone swarm era of cyber
Shown on screen 4 times. Not read aloud.
-
dax@thdxr
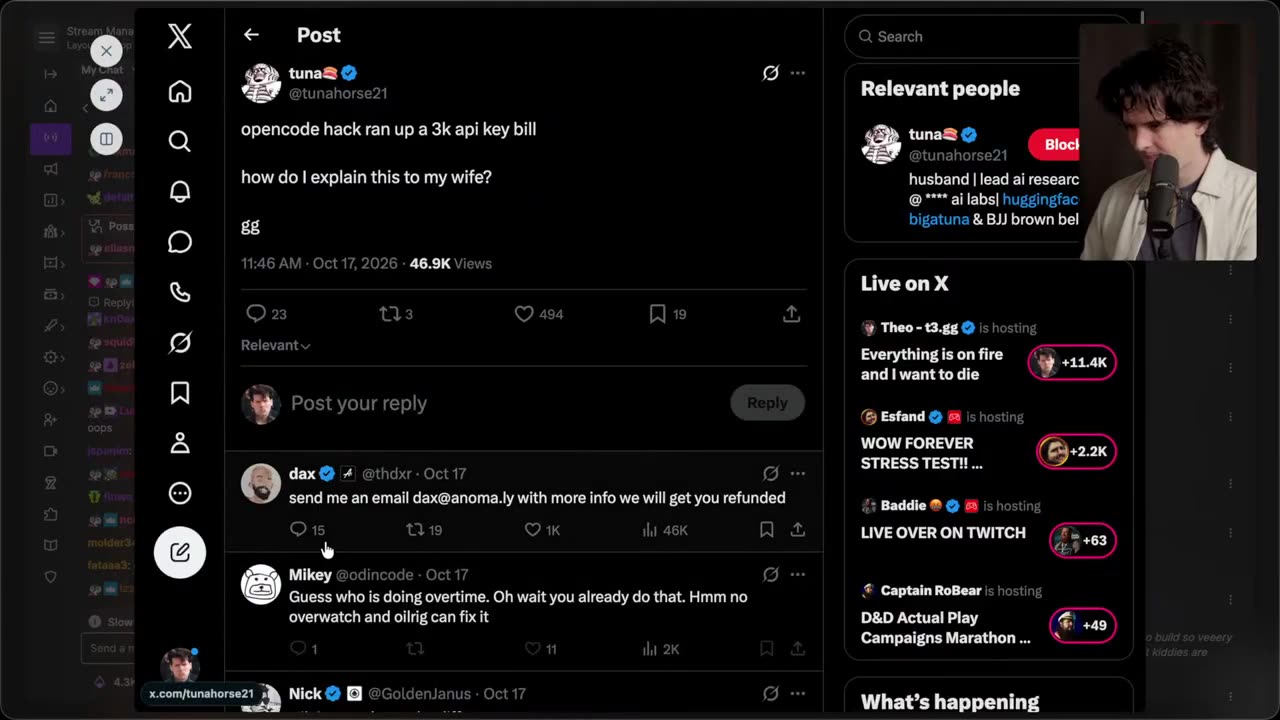
send me an email dax@anoma.ly with more info we will get you refunded 15 · Oct 17
Shown on screen for about 5 seconds. Not read aloud.
-
thdxr@thdxr
Jake on X: "? thdxr @Railwa"
Shown on screen for about 5 seconds. Not read aloud.
-
dax@thdxr
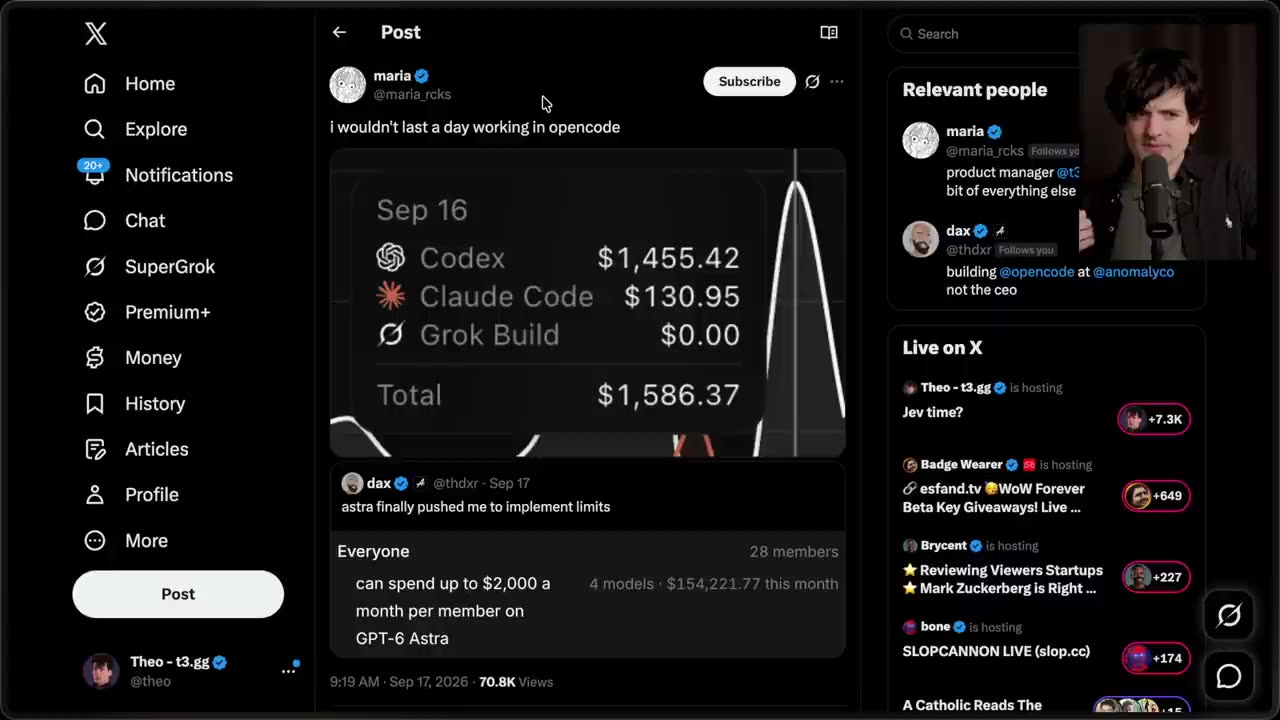
astra finally pushed me to implement limits
Shown on screen for about 21 seconds. Not read aloud.